In short
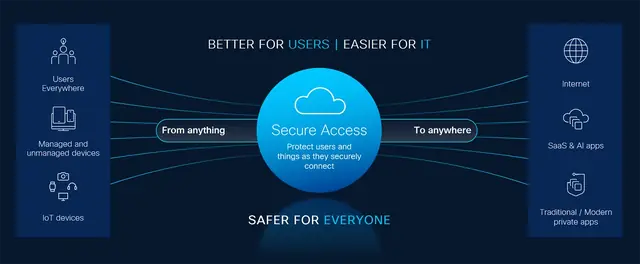
Cisco Umbrella setup means sending DNS, and for SIG customers web and firewall traffic, to Umbrella's cloud. Most organisations point network DNS at Umbrella, add virtual appliances for internal DNS and Active Directory, install the roaming module on laptops, protect Chromebooks, and connect sites by IPsec tunnel for SIG.
Want help with Cisco Umbrella deployment?
We can plan it with you or do it for you. Tell us where you are up to.
Before you start: plan identities and policy
Every deployment method creates an identity in the Umbrella dashboard: a network, a roaming computer, a Chromebook user, a tunnel, a network device, or a user or group from your directory. Policies are applied to identities in order, so the first job is deciding which identities you need and which policy each should get.
A sensible plan answers four questions:
- Which package? DNS Security Essentials and Advantage cover DNS-layer protection; only the SIG packages add the full web proxy, cloud-delivered firewall and network tunnels. See Cisco Umbrella licensing.
- Which networks? Every office, school or site with its own internet breakout needs registering, or an internal DNS path through a virtual appliance.
- Which devices leave the building? Laptops need the roaming module; Chromebooks need their own extension.
- Do you need user names in policy and reports? If so, plan the Active Directory or Microsoft Entra ID (formerly Azure AD) integration early. See Cisco Umbrella SSO and identities.
Bear the lifecycle in mind too. Cisco's end-of-sale date for Umbrella is 31 January 2027, so a new deployment should be designed with the later move to Cisco Secure Access in view. The Cisco Umbrella end of life page has the dates.
The deployment options, in order
Most organisations work through these steps. You will not need all of them, but the order matters: get DNS right first, then extend protection to devices and, if you have SIG, to all web and firewall traffic.
- Point network DNS at Umbrella. Set your router, firewall or DNS server forwarders to the Umbrella DNS servers and register each public IP address as a network identity. This protects every device that uses that network's DNS, including guests and IoT. On Windows DNS servers, Umbrella DNS forwarders replace your existing forwarders, so internal zones stay local and only external lookups go to Umbrella.
- Deploy virtual appliances where you run internal DNS. If you have Windows DNS or Active Directory, put two or more Umbrella virtual appliances in front of it, so internal names keep resolving locally and reports show internal IP addresses.
- Add the AD Connector or a cloud directory. This gives you users and groups for policy and reporting.
- Install the roaming module on laptops. The Cisco Umbrella client, now the Umbrella Roaming Security Module in Cisco Secure Client (formerly AnyConnect) protects Windows and macOS devices on any network.
- Protect Chromebooks. Use Cisco Security for Chromebook, which replaced the legacy Umbrella Chromebook clients.
- For SIG, build tunnels from each site. Umbrella IPsec tunnels from firewalls, routers and SD-WAN send all internet-bound traffic to the secure web gateway (opens in a new tab) and cloud-delivered firewall. Cisco Meraki has its own options; see Cisco Umbrella Meraki integration.
- Use PAC files or proxy chaining where tunnels do not fit. For SIG, browsers can be pointed at the Umbrella web proxy with a PAC file, or an existing on-premises proxy can forward to it. Proxy chaining is for network deployments only: Cisco does not support sending proxy-chained traffic through an IPsec tunnel.
- Test, then tighten. Check blocks and allows with Cisco's test destinations, review Umbrella reporting, then move from a monitoring-style policy to your full content filtering policy.
Which method covers what
Each method protects a different slice of your estate. Use this to check for gaps.
| Method | What it protects | Packages | Identity it creates |
|---|---|---|---|
| Network DNS forwarding | Every device using that network's DNS | All | Network |
| Virtual appliance | Internal DNS clients, with internal IP visibility | All | Internal network, plus AD users with the connector |
| Roaming module (Secure Client) | Windows and macOS laptops on any network | All (web module needs SIG) | Roaming computer, plus user |
| Cisco Security for Chromebook | ChromeOS devices (DNS for the OS; web proxy in Chrome for SIG) | All (web proxy needs SIG) | Chromebook user |
| IPsec tunnel | All internet-bound traffic from a site | SIG only | Tunnel |
| PAC file or proxy chaining | Browser web traffic | SIG only | Depends on authentication |
| Network device integrations (e.g. Meraki access points) | DNS from clients on that device, SSID or group policy | Varies by integration | Network device |
The table reflects Cisco's package information: virtual appliances and roaming protection are in every package, while network tunnels and the full web proxy are SIG-only. Check the exact entitlement for your package on the packages page. Cisco's own configuration guide for each method is in its Umbrella DNS and SIG user guides; our pages for each child topic summarise the steps.
Not sure which package applies to you? Ask us
Tell us about your organisation and we will point you to the right package.
Common pitfalls
- Only one resolver configured. Always use two different Umbrella addresses so a single path failure does not break DNS.
- Internal names breaking. If clients use Umbrella directly, internal domains will not resolve. Keep internal DNS local, through a virtual appliance or your own DNS servers forwarding only external queries.
- Clients bypassing DNS. Devices with hard-coded resolvers or browser DNS over HTTPS (opens in a new tab) can sidestep network DNS. Block outbound DNS to other resolvers at the firewall and manage browser settings.
- Old clients left in place. The standalone Umbrella Roaming Client reached its last date of support on 2 April 2025. Move to Secure Client.
- Tunnels with no backup. Some Umbrella data centres, Manchester among them, have no automatic IPsec failover and must have a backup tunnel. Even where failover is automatic, as with London, Cisco still recommends one.
- Policies in the wrong order. Umbrella evaluates policies from the top down and stops at the first match, falling back to the Default policy, so put the most specific identities at the top.
Planning for Cisco Secure Access
Cisco Secure Access is Cisco's named successor to Umbrella. It uses Cisco Secure Client on devices, connects sites by IPsec tunnel and draws users from the same kinds of directory. Cisco provides an automated upgrade manager for moving Umbrella organisations across, which needs an active Secure Access subscription and a claim code. Deploying Umbrella cleanly now, with documented identities, policies and tunnels, makes that move far easier later. Our Umbrella to Secure Access migration guide covers the steps, and Cisco Secure Access (opens in a new tab) explains the successor platform.
Prefer a hand with this?
We can help you plan it and set it up, alongside your own team.
Our Cisco Umbrella deployment service
We deploy Umbrella for businesses, schools, trusts and public sector organisations, from a single office to multi-site estates.
- Design: package choice, identity plan and policy order
- Network DNS, virtual appliances and the AD Connector or Entra ID sync
- Secure Client packaging and roll-out through Microsoft Intune, Group Policy or your RMM tool
- Cisco Security for Chromebook configuration in the Google Admin console
- IPsec tunnels from Cisco Meraki, Cisco Secure Firewall and other platforms
- Testing, handover documentation and ongoing support
Once you are live, Forever Group's Cisco Umbrella support (opens in a new tab) service can run it day to day. Contact us to scope a deployment or review an existing one.
Sources (checked 11 November 2026): Cisco's roaming client end-of-life notice (opens in a new tab) for the 2 April 2025 last date of support; its guide to deploying virtual appliances for two per site; and its end-of-life notice for the Umbrella dates.
Explore Deployment
 Roaming clientThe Umbrella Roaming Security Module in Cisco Secure Client: protection for laptops off the network.
 Virtual applianceUmbrella VAs forward external DNS to Umbrella, keep internal names local and add internal IP and AD visibility.
 ChromebooksCisco Security for Chromebook: Umbrella DNS protection for ChromeOS and web proxy protection in Chrome.
 IPsec tunnelsConnect sites to Umbrella SIG with IKEv2 IPsec tunnels from firewalls, routers and SD-WAN.Meraki integrationHow Cisco Meraki connects to Umbrella: DNS integration, MX IPsec tunnels to SIG and the SD-WAN Connector.
 Identities and SAMLUmbrella identities: networks, devices, tunnels, and users from Active Directory or Entra ID, plus SAML.
 ReportingThe Umbrella dashboard, its reports, scheduled emails, the Reporting API and S3 log export.
How Forever Systems can help with Cisco Umbrella
We can supply and deploy Cisco Umbrella, help you run it, and plan the move to its successor, Cisco Secure Access.
- Package selection: Umbrella DNS or SIG, Essentials or Advantage, plus add-ons, matched to your users, sites and compliance needs
- Deployment: network DNS forwarding, virtual appliances, the roaming module in Cisco Secure Client, Chromebooks, IPsec tunnels from Cisco Meraki and other firewalls, and Active Directory, Entra ID or SAML identity integration
- Policy design: security categories, content filtering for schools and businesses, allow and block lists, and reporting
- Migration planning from Umbrella to Cisco Secure Access ahead of Cisco's end-of-sale and end-of-support dates
- Ongoing help: reporting, policy tuning, renewals and licence changes
Forever Systems is a Cisco Partner and also supplies the wider Cisco Secure portfolio, including Cisco Secure Access.
Frequently asked questions
How do I set up Cisco Umbrella?
Start by registering each site's public IP address as a network identity in the Umbrella dashboard and pointing that network's DNS at the Umbrella resolvers. Test with Cisco's test destinations, then add virtual appliances for internal DNS, a directory integration, the Umbrella module in Cisco Secure Client for laptops, Cisco Security for Chromebook and, for SIG, IPsec tunnels.
How do I configure DNS forwarders for Umbrella?
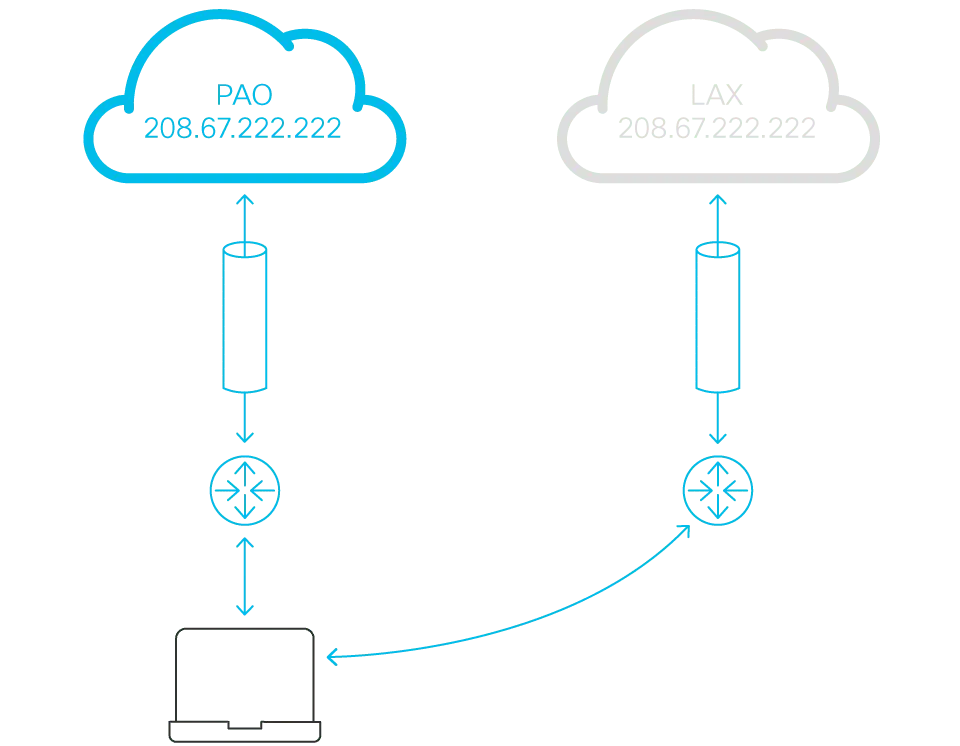
On each internal DNS server, replace the existing forwarders with the Umbrella addresses 208.67.222.222 and 208.67.220.220 (and 2620:119:35::35 and 2620:119:53::53 for IPv6), leave clients pointing at your internal DNS, and register the site's public IP as a network identity. For per-device and per-user reporting, put Umbrella virtual appliances in front instead. See Umbrella DNS servers.
Where is the Cisco Umbrella configuration guide?
Cisco publishes Umbrella's configuration documentation as user guides, including the Umbrella DNS user guide and the Umbrella SIG user guide, plus platform guides for tunnels. This page puts the steps in the order most organisations follow and links to our guide for each method.
How long does it take to deploy Cisco Umbrella?
Pointing one network's DNS at Umbrella is a small change. A full deployment with virtual appliances, directory integration, roaming modules and tunnels depends on the number of sites and devices, and we run it as a project with a pilot group first.
Do I need the roaming client if I already forward DNS to Umbrella?
Network forwarding only protects devices while they use that network. Laptops that go home or onto public Wi-Fi need the Umbrella Roaming Security Module in Cisco Secure Client to stay protected.
Can I deploy Umbrella without changing my firewall?
For DNS-layer protection, yes: you change DNS forwarders, not firewall rules. Blocking outbound DNS to other resolvers is still recommended. SIG tunnels do require configuration on the firewall or router.
Is it still worth deploying Umbrella in 2026?
Existing subscriptions continue to be supported until 31 January 2029, and Cisco's end of sale is 31 January 2027. New buyers should compare Umbrella with Cisco Secure Access before committing, and we can help you decide.
Still have a question about Cisco Umbrella deployment?
Ask us and a member of our team will get back to you.