
In short
Umbrella DNS filtering, the content filtering in every Cisco Umbrella package, blocks websites by category, custom block list or domain before a connection is made, using DNS. Policies are matched to identities in order, with a customisable block page, optional bypass codes, and SafeSearch for Google, YouTube and Bing. URL-level filtering needs the intelligent proxy or the SIG secure web gateway.
Get a quote for Cisco Umbrella content filtering
Tell us roughly how many users or sites you have and we will come back to you with options and a quote.
How Umbrella filters content
Every Umbrella package starts with DNS-layer filtering. When a device looks up a domain, Umbrella checks it against the security and content categories in the matching policy. If the domain is allowed, Umbrella returns the real address; if not, it returns the address of a block page, so the browser never reaches the site. Because this happens at the DNS lookup, it works for every application and port, and it adds very little delay. Our what is Cisco Umbrella? guide explains the mechanism in more depth.
DNS has one built-in limit: it only ever sees the domain name. Cisco's own documentation notes that content categories classify at the domain level, so a domain that hosts many kinds of content is filtered as whatever the whole domain is categorised as. To act on individual pages you need a proxy:
| Filtering layer | What it sees | Packages |
|---|---|---|
| DNS-layer filtering | Domain names only | All four packages |
| Intelligent proxy | Full URLs and files, but only for domains Cisco considers risky, plus URL entries in your destination lists | DNS Security Advantage, SIG Essentials, SIG Advantage |
| Secure web gateway (opens in a new tab) (full proxy) | Every web request, including decrypted HTTPS, with URL and file controls | SIG Essentials, SIG Advantage |
That is the practical difference between DNS filtering and web filtering: DNS filtering decides by domain before any connection is made, while web filtering through a proxy can judge each page and file. For the general technology across vendors, see our guide to DNS filtering (opens in a new tab).
The Umbrella packages page compares the tiers in full, and the Umbrella secure web gateway page covers HTTPS inspection.
In the product
Not sure which package fits? Ask us
Tell us what you need and we will recommend the right package for your organisation, with a quote.
Building a DNS policy, step by step
Umbrella's DNS policy wizard follows the same order every time. A sensible build for a typical organisation looks like this:
- Choose the identities the policy applies to: networks, sites, roaming computers, Chromebooks, or Active Directory and Entra ID users and groups (see Umbrella identities and SAML).
- Set security categories. Malware, command and control and phishing are on by default, and Cisco suggests finding the right combination of the others for your organisation (see Umbrella DNS categories).
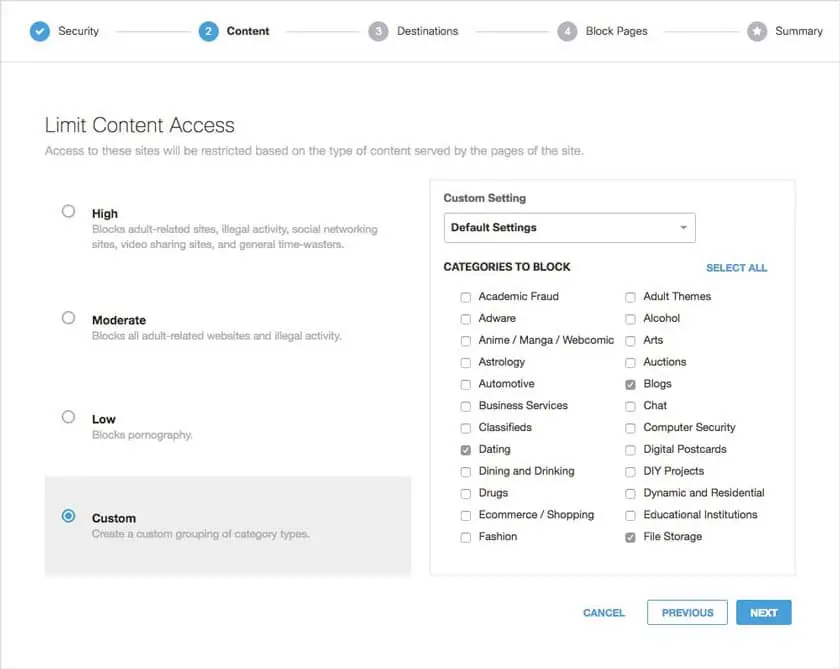
- Pick a content preset or build a custom one. Umbrella offers Low, Moderate and High presets that build on each other, plus Custom, which exposes every category.
- Add application settings if you want to allow or block specific cloud apps.
- Attach destination lists for the domains you always want to allow or always want to block.
- Turn on file inspection if your package includes it, so files from risky domains are scanned before download.
- Choose the block page appearance and any bypass users or codes.
- Name the policy, save it and set its position in the policy list.
Policy order matters. Umbrella reads your DNS policies from the top down, applies the first one that matches the identity, and stops. If nothing matches, the Default policy applies. The Default policy cannot be deleted and catches any identity no other policy matches, so it makes sense to set it as either your most restrictive policy or the one most users should get, then layer more specific policies (for example, a students policy or a Chromebook policy) above it as exceptions. Use Umbrella's policy tester to check which policy an identity will hit for a given domain before you go live, and allow up to about five minutes for a saved policy to take effect across Umbrella's network.
Allow lists, block lists and category presets
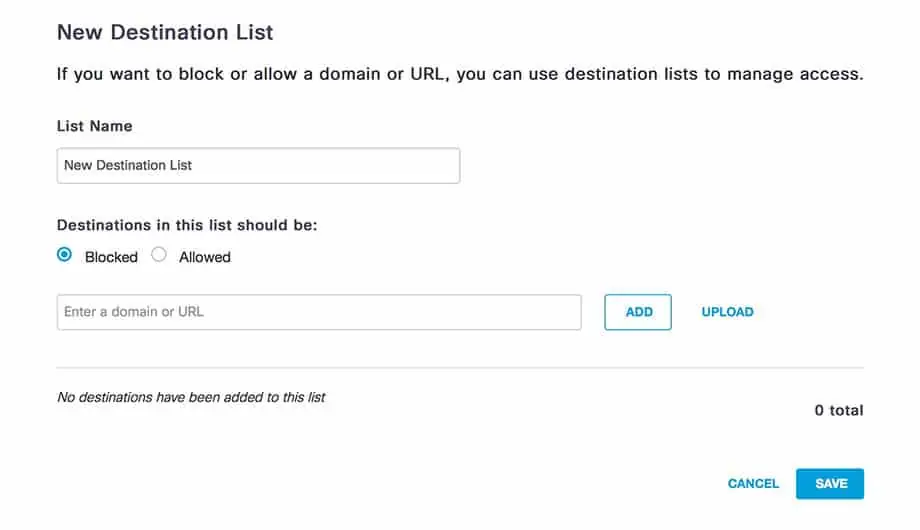
Destination lists are where you record local decisions: a supplier portal that a strict category would block, or a domain your safeguarding team has asked you to stop. Lists can be added in bulk and exported to CSV, which makes them easy to review. In DNS policies they work at the domain level; URL entries only take effect where a proxy is in the path, which means the intelligent proxy on DNS Security Advantage or the secure web gateway on the SIG packages.
The Low, Moderate and High presets are a fast way to start. In Cisco's current Talos-based category set, Low covers pornography, adult and extreme content, filter avoidance and encrypted DNS; Moderate adds areas such as gambling, illegal drugs, hate speech, weapons, terrorism and violent extremism, dating and alcohol; High adds time-wasters such as social networking, streaming video, games, chat and web-based email. Many organisations start from a preset and then switch to Custom to fine-tune it. Expect to revisit this after a week or two of real traffic in the Umbrella reporting tools.
Is Cisco Umbrella content filtering the right fit for you?
We will check it against your systems and requirements and recommend the right option.
SafeSearch and YouTube Restricted Mode
Umbrella can force SafeSearch without a proxy. The major search engines publish dedicated SafeSearch hostnames, and when SafeSearch is enabled in a policy Umbrella answers lookups for their main domains with a CNAME pointing at those hostnames. Cisco supports this method for Google, YouTube and Bing.
What users see once it is working:
- Google: results show that SafeSearch is on, and switching it off in settings has no effect
- YouTube: Restricted Mode is shown as enabled by the network administrator
- Bing: SafeSearch is set to Strict and cannot be changed
Two points from Cisco's documentation help when you set it up. Because SafeSearch is a redirect rather than a block, it does not appear in Umbrella reports. And if you enable application control for Google apps in the same policy, SafeSearch stops working, so test the combination before rolling it out.
Block pages and bypass options
When Umbrella blocks a request it shows a block page. You can keep the Umbrella default or create custom appearances and link them to particular policies. A custom block page can:
- use one message for every kind of block, or different messages for security and content blocks
- include the blocked domain and the user's external IP address through built-in variables
- carry your own logo in place of the Umbrella logo
- redirect to a page you host, such as your acceptable-use policy
- if it does not redirect, include a contact form so users can ask an administrator to review the block; the feedback tells you the identity, the destination and the policy that blocked it
For legitimate exceptions there are two bypass routes. Bypass users are existing Umbrella accounts that can sign in from the block page to get past blocks for the selected categories or destination lists. Bypass codes give anyone who has the code access for a set period; set an expiry, or the code expires within an hour by default. A bypass code unblocks only the domain the user is trying to reach, not the whole category, so Cisco notes it is not suited to web apps that need several domains unblocked, such as Gmail or Dropbox; use application settings or a destination list for those. Neither route can override a security block such as malware or phishing, and both only work when enabled on the policy that matches the identity seeing the block page.
Which package do you need, and what about end of sale?
If domain-level filtering with SafeSearch is enough, DNS Security Essentials covers it. If you need to block individual URLs on risky domains, DNS Security Advantage adds the intelligent proxy. If you need full URL filtering for all web traffic, file type controls or tenant controls, you need an Umbrella SIG package. Schools should also read our guide to appropriate filtering for schools.
Cisco has announced end of sale for Umbrella SIG and DNS on 31 January 2027, with renewals possible until 31 January 2028 and support ending on 31 January 2029. Much of the policy you build now can carry across: Cisco's Upgrade Manager copies Umbrella DNS, web and firewall policies into Cisco Secure Access (opens in a new tab) as internet access rules, although some items, such as block page bypass users and codes, are not copied, and multi-org customers should confirm the current scope with Cisco. See our Umbrella end of life guide for the full timeline.
Forever Systems turns acceptable-use policies into working Umbrella configurations: category selection, destination lists, block page wording, bypass arrangements and policy order, followed by a review once real traffic is flowing. Contact us to arrange a policy review.
Sources (checked 11 November 2026): Cisco's Umbrella DNS guide on policy precedence (opens in a new tab), security categories, SafeSearch and bypass codes; and its end-of-life notice for the Umbrella dates.
Cisco Umbrella content filtering pricing
Content filtering across Umbrella's categories comes with every package, so the cost depends on the package rather than on filtering itself. Page-level control needs the intelligent proxy in DNS Security Advantage or the secure web gateway in the SIG packages, and that choice is what moves the price.
Our Cisco Umbrella pricing page sets out how pricing works.
Get a quote for Cisco Umbrella content filtering
Tell us what you need and we will come back to you with a quote.
Explore Content filtering
How Forever Systems can help with Cisco Umbrella
We can supply and deploy Cisco Umbrella, help you run it, and plan the move to its successor, Cisco Secure Access.
- Package selection: Umbrella DNS or SIG, Essentials or Advantage, plus add-ons, matched to your users, sites and compliance needs
- Deployment: network DNS forwarding, virtual appliances, the roaming module in Cisco Secure Client, Chromebooks, IPsec tunnels from Cisco Meraki and other firewalls, and Active Directory, Entra ID or SAML identity integration
- Policy design: security categories, content filtering for schools and businesses, allow and block lists, and reporting
- Migration planning from Umbrella to Cisco Secure Access ahead of Cisco's end-of-sale and end-of-support dates
- Ongoing help: reporting, policy tuning, renewals and licence changes
Forever Systems is a Cisco Partner and also supplies the wider Cisco Secure portfolio, including Cisco Secure Access.
Frequently asked questions
Can Cisco Umbrella block specific URLs rather than whole websites?
Not with DNS alone, because DNS only sees the domain name. URL-level blocking needs a proxy: the intelligent proxy in DNS Security Advantage (for domains it proxies) or the secure web gateway in SIG Essentials and SIG Advantage, which inspects all web traffic.
What is the difference between DNS filtering and web filtering?
DNS filtering decides by domain name at the lookup, before any connection starts, so it covers every app and port but cannot judge a single page. Web filtering through a proxy, such as Umbrella's intelligent proxy or secure web gateway, sees full URLs and files, including decrypted HTTPS. Umbrella DNS filtering is in every package; full web filtering needs SIG.
How do I allow a site in Cisco Umbrella?
Add the domain to an allow destination list and attach that list to the policy that applies to the users concerned. Allow lists work at domain level in DNS policies; URL entries need a proxy in the path. For a one-off exception, a bypass code unblocks just the requested domain for a set time.
How do I customise the Cisco Umbrella block page?
Create a custom block page appearance in the dashboard and link it to a policy. You can use different messages for security and content blocks, show the blocked domain, add your logo, redirect to your acceptable-use page, or include a form so users can ask for a review.
How do I enforce YouTube restricted mode with Cisco Umbrella?
Turn on SafeSearch in the DNS policy. Umbrella then answers lookups for Google, YouTube and Bing with their SafeSearch hostnames, so YouTube shows Restricted Mode as enabled by the network administrator. The same setting enforces Google SafeSearch and Bing Strict SafeSearch. The redirect does not show in Umbrella reports, and Cisco notes it stops working if application control for Google apps is enabled in the same policy.
Can users bypass the Umbrella block page?
Only if you allow it. You can set up bypass users who sign in from the block page, or bypass codes that expire after a set time (within an hour by default) and unblock only the domain being requested. Both are limited to the categories or destination lists you choose. Security blocks such as malware and phishing cannot be bypassed.
How does Umbrella decide which policy applies?
Umbrella checks policies in the order you set, from the top, and applies the first one that matches the identity making the request. If none match, the Default policy applies. Put specific policies above general ones and check the result with the policy tester.
Does Umbrella DNS filtering work on HTTPS sites?
DNS filtering works for HTTPS sites because it acts on the domain lookup before any encrypted connection starts. Inspecting the content of HTTPS traffic, such as individual URLs or files, needs the intelligent proxy or secure web gateway with the Umbrella root certificate installed on devices.
Still have a question about Cisco Umbrella content filtering?
Ask us and a member of our team will get back to you.
Explore Cisco Umbrella
 Umbrella for schoolsDNS filtering for schools, colleges and trusts: on site, at home and on Chromebooks.
 Secure web gatewayFull cloud web proxy with HTTPS inspection, file scanning and tenant controls.
 DNS Security AdvantageAdds the intelligent proxy for risky domains and Umbrella Investigate.
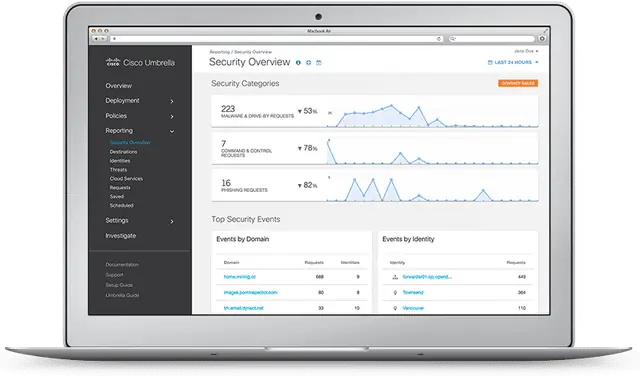 ReportingThe Umbrella dashboard, its reports, scheduled emails, the Reporting API and S3 log export.
 Identities and SAMLUmbrella identities: networks, devices, tunnels, and users from Active Directory or Entra ID, plus SAML.