
In short
Cisco Umbrella reporting is built into the Umbrella dashboard at dashboard.umbrella.com. It includes Activity Search, Security Activity, Top Destinations, Top Identities and App Discovery reports, scheduled email reports, a Reporting API, and log export to a Cisco-managed or your own Amazon S3 bucket for SIEM tools.
Get a quote for Cisco Umbrella reporting
Tell us roughly how many users or sites you have and we will come back to you with options and a quote.
The Umbrella dashboard
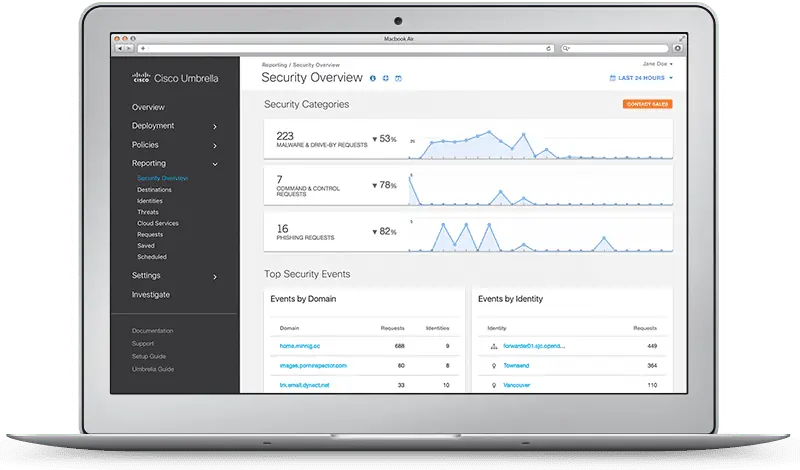
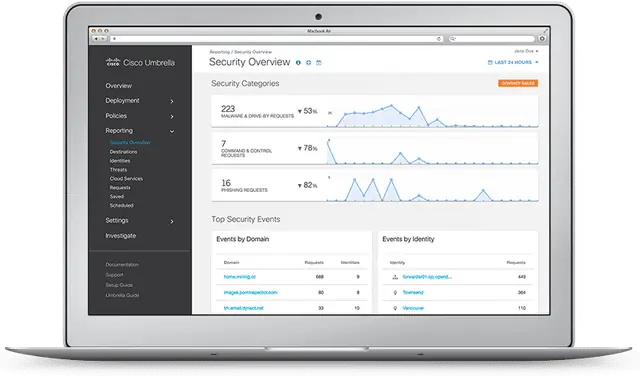
Administrators sign in to the Umbrella dashboard at dashboard.umbrella.com. Reporting starts as soon as traffic reaches Umbrella, whether through network DNS, the roaming module, a virtual appliance or a tunnel. The main reports are:
| Report | What it shows |
|---|---|
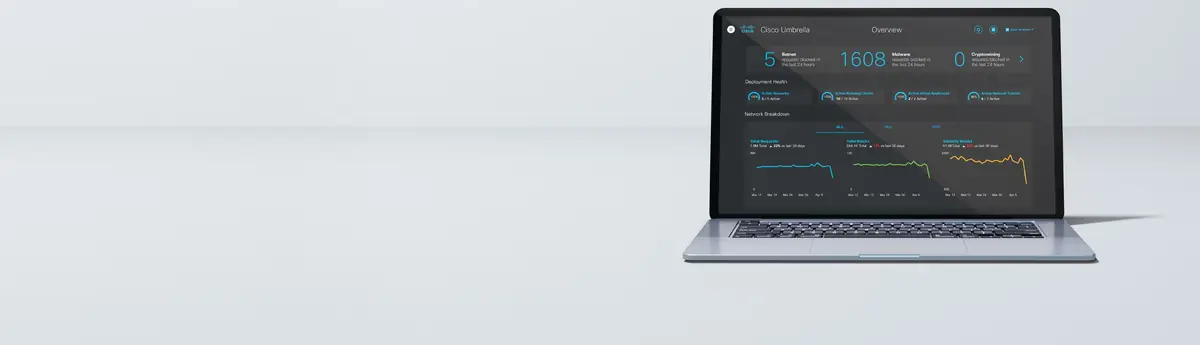
| Overview | A snapshot of your environment's security activity |
| Security Activity | Malware, phishing and other security-category events, filterable by identity, destination and source IP |
| Activity Search | Every logged request, filterable by identity, destination, source IP, response, content category and security category |
| Top Threats | Blocked and allowed threats your organisation may have been exposed to |
| Total Requests and Activity Volume | Request trends over time, broken down by security category and result |
| Top Destinations, Top Categories, Top Identities | The most requested domains, the busiest content categories and the identities generating most traffic |
| App Discovery | The cloud applications in use, with risk information (see Umbrella CASB) |
| Admin Audit Log | Every configuration change made by your Umbrella administrators |
Reports are more useful when identities are named. With Active Directory, Entra ID or Google Workspace integration, reports show people and groups rather than IP addresses; see Umbrella identities and SAML.
In the product
Not sure which option fits? Ask us
Tell us what you need and we will recommend the right option for your organisation, with a quote.
Using Activity Search day to day
Activity Search is where most troubleshooting happens. Typical uses:
- A user says a site is blocked. Filter by their identity and the domain, check the response and the category, and decide whether to add it to an allow list or dispute the category.
- A security alert from another tool. Filter by the device or IP to see what it looked up before and after the alert.
- Policy tuning. Filter on a content category to see who is hitting it before tightening or relaxing a rule.
- Evidence for a review. Save the columns and filters you use regularly, then export to CSV or schedule the report.
From an Activity Search entry you can open full details and raise a categorisation dispute (see Umbrella DNS categories). On DNS Security Advantage and the SIG packages, analysts can pivot from a suspicious domain into Umbrella Investigate for its history and related infrastructure.
Scheduled reports and data retention
Most reports can be emailed on a schedule, daily, weekly or monthly. Each email includes an HTML version of the report, a zipped CSV of the full data set and a link back to the dashboard. Cisco allows up to 100 scheduled reports per organisation, and an emailed report is limited to 10,000 rows (opens in a new tab), so apply filters before you schedule: a weekly Top Categories report for a manager, or a security summary for the IT team. Reports are sent from an opendns.com address, so if they do not arrive, check your email security (opens in a new tab) quarantine.
Cisco's documentation currently describes retention like this:
| Data | Retention described by Cisco |
|---|---|
| Total Requests, Top Destinations, Top Categories, Top Identities, Activity Volume | One calendar year |
| Activity Search and Security Activity | Data kept for 90 days, searched in windows of up to 30 days |
| Cisco-managed S3 log export | Your choice of 7, 14 or 30 days |
For current data retention information, Cisco points to its Umbrella Offer Disclosure on the Cisco Trust Portal, so check it if retention matters for compliance. If you need logs for longer, export them to your own storage.
Is Cisco Umbrella reporting the right fit for you?
We will check it against your systems and requirements and recommend the right option.
Exporting logs to S3 and your SIEM
Umbrella can write its DNS, URL and IP event logs to Amazon S3 as compressed CSV files, uploaded about every ten minutes, in two ways:
- A Cisco-managed bucket: choose a region and a retention period of 7, 14 or 30 days; anything older is purged and cannot be recovered. Cisco encrypts the data at rest with Amazon S3-managed keys and shows you the access keys once, at set-up, so store them safely; if they are lost they must be regenerated.
- Your own bucket: Umbrella writes to an S3 bucket you control, with a bucket policy granting it access, and you set your own retention.
Most SIEM and log platforms can collect from S3, which is the usual route for correlating Umbrella events with firewall, endpoint and identity logs. Cisco lists S3 log export in all four Umbrella packages.
For UK GDPR planning, note that Umbrella stores event data in a data warehouse in North America (Cisco's California location) by default, and you can change the location to Europe from the dashboard. Configuration data, such as policies and audit logs, stays in California regardless. Existing logs do not move when you change location, reports only use data from the current location, and Cisco recommends against switching back and forth, so decide early.
The Reporting API
The Umbrella Reports API gives programmatic access to the same reporting data, so you can pull Umbrella activity and summaries into your own dashboards, ticketing or automation. Its paths sit under api.umbrella.com/reports/v2, and Cisco groups the endpoints into reporting, App Discovery, API usage reports and provider consoles. Access uses API keys created in the Umbrella dashboard. For continuous, high-volume log collection, S3 export is the more natural route.
Cisco lists the Umbrella API in all four packages. The Multi-org and MSP consoles have their own Console Reporting API keys for reporting across all managed organisations; see Umbrella multi-org and MSP consoles.
Reporting through end of sale, and how we help
Cisco ends sales of Umbrella on 31 January 2027 and support on 31 January 2029. If you need historical Umbrella data for audits or investigations, plan how you will keep it and export what you need before your Umbrella subscription ends. Our Umbrella end of life guide covers the timeline and the Umbrella to Secure Access migration guide covers the move.
Forever Systems sets up useful scheduled reports, connects Umbrella logs to your SIEM, and can review your reports monthly as part of a managed service. Contact us to discuss reporting or a managed service.
Sources (checked 11 November 2026): Cisco's Umbrella DNS guide on scheduled reports, report retention, logging to Amazon S3, the Cisco-managed S3 bucket and changing data warehouse location; and its end-of-life notice for the Umbrella dates.
Cisco Umbrella reporting pricing
Umbrella's reports and log export come with the packages, so reporting adds no separate licence. Where a package includes Cisco-managed S3 log storage, Cisco offers 7, 14 or 30 days of retention; the package and the people covered set the price.
Our Cisco Umbrella pricing page sets out how pricing works.
Get a quote for Cisco Umbrella reporting
Tell us what you need and we will come back to you with a quote.
How Forever Systems can help with Cisco Umbrella
We can supply and deploy Cisco Umbrella, help you run it, and plan the move to its successor, Cisco Secure Access.
- Package selection: Umbrella DNS or SIG, Essentials or Advantage, plus add-ons, matched to your users, sites and compliance needs
- Deployment: network DNS forwarding, virtual appliances, the roaming module in Cisco Secure Client, Chromebooks, IPsec tunnels from Cisco Meraki and other firewalls, and Active Directory, Entra ID or SAML identity integration
- Policy design: security categories, content filtering for schools and businesses, allow and block lists, and reporting
- Migration planning from Umbrella to Cisco Secure Access ahead of Cisco's end-of-sale and end-of-support dates
- Ongoing help: reporting, policy tuning, renewals and licence changes
Forever Systems is a Cisco Partner and also supplies the wider Cisco Secure portfolio, including Cisco Secure Access.
Frequently asked questions
How do administrators sign in to the Cisco Umbrella dashboard?
Administrators sign in to the Umbrella dashboard at dashboard.umbrella.com with the account their organisation has set up for them. Organisations can also turn on SAML single sign-on so administrators sign in through their own identity provider, and multi-org or MSP console administrators sign in to the parent console. If you have lost access, ask another administrator in your organisation, or your Umbrella provider, to check your account.
How do I see Cisco Umbrella reports?
Sign in to the Umbrella dashboard at dashboard.umbrella.com and open the Reporting section: Activity Search, Security Activity, Top Destinations, Top Identities and App Discovery, among others. Most reports can also be emailed daily, weekly or monthly with an HTML summary and a zipped CSV.
Does Cisco Umbrella have a reporting API?
Yes. The Umbrella Reports API gives programmatic access to the same reporting data for your own dashboards, ticketing or automation, and Cisco lists the Umbrella API in all four packages. Multi-org and MSP consoles have their own Console Reporting API keys.
How do I monitor Umbrella DNS activity?
Use Activity Search to follow requests by identity, destination or category in near real time, schedule Top Categories or Security Activity reports by email, and export DNS, URL and IP logs to Amazon S3 so your SIEM can alert on them.
How long does Cisco Umbrella keep data?
Cisco's documentation describes one calendar year for summary reports such as Top Destinations and Total Requests, and 90 days for Activity Search and Security Activity, searched in windows of up to 30 days. Cisco-managed S3 export keeps logs for 7, 14 or 30 days. For current retention information, Cisco points to its Umbrella Offer Disclosure on the Cisco Trust Portal.
Can I schedule Umbrella reports by email?
Yes. Reports such as Overview, Activity Search, Top Threats, Top Destinations, Top Categories and Top Identities can be emailed daily, weekly or monthly, with an HTML summary and a zipped CSV. Cisco allows up to 100 scheduled reports per organisation, and each emailed report is limited to 10,000 rows.
Can Cisco Umbrella send logs to a SIEM?
Yes, through Amazon S3. Umbrella writes event logs to a Cisco-managed or customer-owned S3 bucket about every ten minutes, and most SIEM platforms can collect from there. Cisco lists S3 log export in all four Umbrella packages.
Where is Cisco Umbrella data stored?
Event data goes to a data warehouse in North America by default, and you can choose Europe instead. Configuration data such as policies and audit logs stays in Cisco's California location whichever you choose.
Still have a question about Cisco Umbrella reporting?
Ask us and a member of our team will get back to you.
Explore Cisco Umbrella
 Multi-org and MSPManage many Umbrella organisations from one console, or have us manage Umbrella for you.
 InvestigateThreat intelligence console and API for researching domains, IPs and files.
 Content filteringBuild an acceptable-use policy with categories, allow and block lists, SafeSearch and block pages.
 CASBDiscover the cloud apps your people use, judge their risk and control them.
 DNS Security AdvantageAdds the intelligent proxy for risky domains and Umbrella Investigate.