

In short
Cisco Umbrella Investigate is a threat intelligence console and API built on the DNS data Umbrella sees. Analysts look up domains, IPs, ASNs and file hashes to see risk scores, WHOIS, passive DNS and related infrastructure. It is included in DNS Security Advantage and both SIG packages; extra users and API tiers are sold separately.
Get a quote for Cisco Umbrella Investigate
Tell us roughly how many users or sites you have and we will come back to you with options and a quote.
What Umbrella Investigate is
Umbrella resolves DNS for a very large number of users worldwide, and Cisco Talos (opens in a new tab) combines that view with its other threat research. Umbrella Investigate opens that intelligence to your own team. Instead of asking "is this domain blocked?", an analyst can ask "what is this domain, who registered it, what else lives on the same infrastructure, and has malware been seen talking to it?"
It comes in two forms:
- The Investigate console, a web interface for interactive research and pivoting during triage or an incident
- The Investigate API, for automated look-ups from a SIEM, SOAR platform or threat intelligence platform (TIP). Cisco publishes a Secure Access Investigate API as its successor
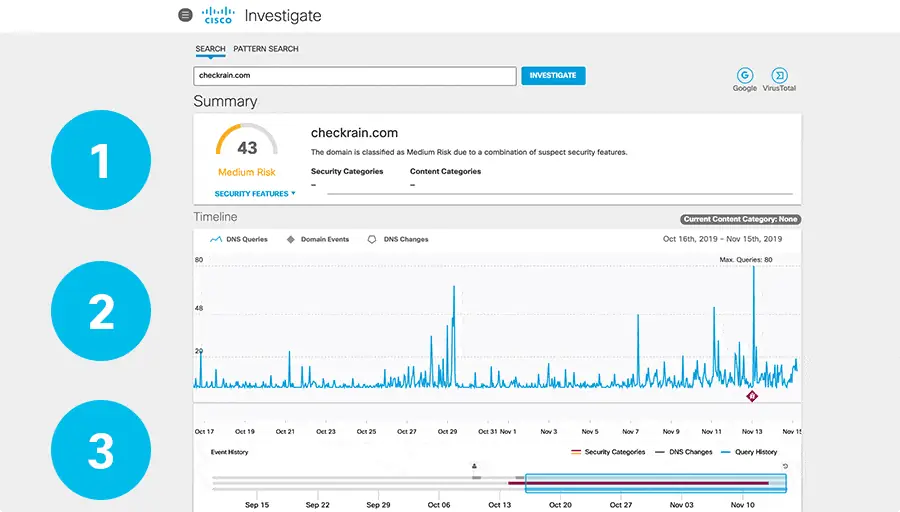
Cisco describes the console as giving security teams interactive access to Umbrella's threat intelligence for incident investigation and response, with threat scores that show what contributed to them and, in its passive DNS view, key events and security categories for a domain over the past five years (Cisco's Investigate page).
What you can look up
Investigate is organised around the things analysts typically hold when they start: a domain, an IP address, an autonomous system number (ASN), an email address from a registration record, or a file hash. Cisco's Investigate API documentation groups the information into:
- Domain status and categorisation, including security categories and content categories
- Security and risk scores that summarise how suspicious a domain looks
- WHOIS records and WHOIS history, with searches by registrant email or nameserver to find other domains registered the same way
- Passive DNS: which IPs a domain has resolved to over time, and which domains point at an IP
- Co-occurring domains, related domains and subdomains, which often reveal the rest of a campaign
- BGP routing information for an IP address or ASN, to place infrastructure in context
- Malware samples associated with a domain, IP, URL or file hash, with their artefacts, connections and behaviours. Cisco notes that sample look-ups need a Cisco Secure Malware Analytics (formerly Threat Grid) licence as well as Investigate
Investigate does not change what Umbrella blocks by itself. Its value is in speeding up decisions: confirming an alert, finding related indicators, and adding them to a destination list or your other controls.
Which packages include Investigate
Cisco's package comparison shows Investigate console access and the on-demand enrichment API as included in DNS Security Advantage, SIG Essentials and SIG Advantage. DNS Security Essentials does not include it. On the older Insights package it was an add-on.
Beyond what the packages bundle, Cisco sells Investigate separately as additional console users and Investigate API tiers (small, medium and large), for security operations teams and service providers who need more users or higher look-up volumes. Education variants also exist. Older Investigate API tiers numbered 1 to 3 were replaced by the small, medium and large tiers when Cisco retired its legacy Umbrella offers in 2025. Exact entitlements vary by package and agreement, so we check your current licence before recommending more. See Umbrella packages compared.
Is Cisco Umbrella Investigate the right fit for you?
We will check it against your systems and requirements and recommend the right option.
Using Investigate with your SIEM and XDR
A typical use of the API is enrichment: when your SIEM or SOAR raises an alert containing a domain or IP, it calls Investigate automatically and attaches the risk score, categorisation and related infrastructure, so the analyst starts with context rather than a bare indicator.
If you use Cisco's own detection and response tools, Umbrella and Investigate data can feed Cisco XDR (opens in a new tab), and sandbox detail comes from Cisco Secure Malware Analytics (opens in a new tab). For Umbrella's own reports and log export, see Umbrella reporting.
End of life and Secure Access Investigate
Investigate is covered by Cisco's Umbrella end-of-life notice. The last day to order is 31 January 2027, renewals and additions are possible until 31 January 2028, and support ends on 31 January 2029.
| Umbrella Investigate product | Migration product |
|---|---|
| Investigate console users | Secure Access Investigate console users |
| Investigate API (small, medium, large) | Secure Access Investigate API, matching size |
| Investigate Integration API and Console | No migration product |
| Some Education and package-specific Investigate API and console products | No migration product |
If your integrations call the Umbrella Investigate API, plan to repoint them at the Secure Access Investigate API, which Cisco serves from a different base address (under api.sse.cisco.com), and test them before support ends. Our Umbrella end of life guide lists every affected item and the migration guide covers the steps.
Not sure which option fits? Ask us
Tell us what you need and we will recommend the right option for your organisation, with a quote.
How we help
Forever Systems can confirm what Investigate access your current Umbrella licence includes, add console users or API capacity where needed, connect the API to your SIEM or SOAR, and plan the move to Secure Access Investigate with the rest of your Umbrella estate. Contact us to discuss your requirements.
Sources (checked 11 November 2026): Cisco's Umbrella Investigate page (opens in a new tab) for the console, risk scores and passive DNS; Cisco's package comparison for the packages that include the console and API; and its end-of-life notice for the dates and the Investigate items with no migration product.
Cisco Umbrella Investigate pricing
Investigate console access is included with DNS Security Advantage and both SIG packages, so for many security teams the price is simply that of the package. Extra console users and the Investigate API tiers (small, medium and large) are bought separately when you need more.
Our Cisco Umbrella pricing page sets out how pricing works.
Get a quote for Cisco Umbrella Investigate
Tell us what you need and we will come back to you with a quote.
How Forever Systems can help with Cisco Umbrella
We can supply and deploy Cisco Umbrella, help you run it, and plan the move to its successor, Cisco Secure Access.
- Package selection: Umbrella DNS or SIG, Essentials or Advantage, plus add-ons, matched to your users, sites and compliance needs
- Deployment: network DNS forwarding, virtual appliances, the roaming module in Cisco Secure Client, Chromebooks, IPsec tunnels from Cisco Meraki and other firewalls, and Active Directory, Entra ID or SAML identity integration
- Policy design: security categories, content filtering for schools and businesses, allow and block lists, and reporting
- Migration planning from Umbrella to Cisco Secure Access ahead of Cisco's end-of-sale and end-of-support dates
- Ongoing help: reporting, policy tuning, renewals and licence changes
Forever Systems is a Cisco Partner and also supplies the wider Cisco Secure portfolio, including Cisco Secure Access.
Frequently asked questions
What is Cisco Umbrella Investigate?
A threat intelligence console and API, built on the DNS data Umbrella sees and Cisco Talos research, for researching domains, IP addresses, ASNs and file hashes during threat hunting (opens in a new tab) and incident response. It shows risk scores, categorisation, WHOIS, passive DNS, co-occurring domains and associated malware, through a console for analysts and an API for automated enrichment.
Which Umbrella packages include Investigate?
Cisco's comparison lists Investigate console access and the on-demand enrichment API in DNS Security Advantage, SIG Essentials and SIG Advantage. DNS Security Essentials does not include it, and extra console users and API tiers are sold separately.
Is there an Umbrella Investigate API?
Yes. The Umbrella Investigate API lets SIEM, SOAR and threat intelligence platforms query domain status and categorisation, security and risk scores, WHOIS, passive DNS, co-occurrences and BGP routes. Sample look-ups also need a Secure Malware Analytics licence. Cisco's successor is the Secure Access Investigate API.
Is Umbrella Investigate end of life?
Yes. It is on Cisco's Umbrella end-of-life notice, with end of sale on 31 January 2027 and last support on 31 January 2029. Most console and API products migrate to Secure Access Investigate, but some, including the Investigate Integration API and Console, have no migration product.
Still have a question about Cisco Umbrella Investigate?
Ask us and a member of our team will get back to you.
Explore Cisco Umbrella
 DNS Security AdvantageAdds the intelligent proxy for risky domains and Umbrella Investigate.
 PackagesDNS Security and SIG packages side by side, with add-ons and Secure Access equivalents.
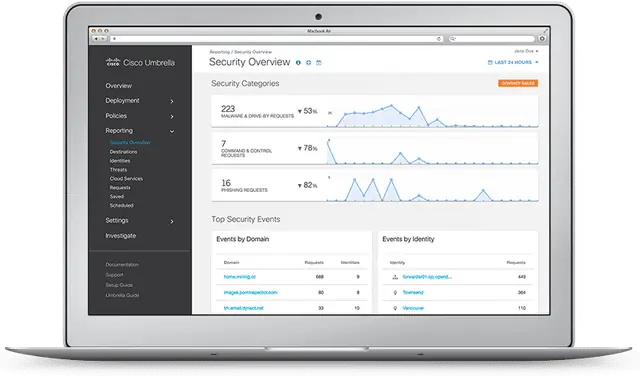 ReportingThe Umbrella dashboard, its reports, scheduled emails, the Reporting API and S3 log export.
 End of lifeEvery end-of-life milestone, what is affected and what has no replacement.