
In short
The Umbrella DNS servers are the anycast resolvers 208.67.222.222 and 208.67.220.220 for IPv4 and 2620:119:35::35 and 2620:119:53::53 for IPv6, with DNS over HTTPS at doh.umbrella.com. Use only Umbrella resolvers, as two different addresses, then register your network as an identity in the Umbrella dashboard.
Get a quote for Cisco Umbrella deployment
Tell us roughly how many users or sites you have and we will come back to you with options and a quote.
The Umbrella DNS server addresses
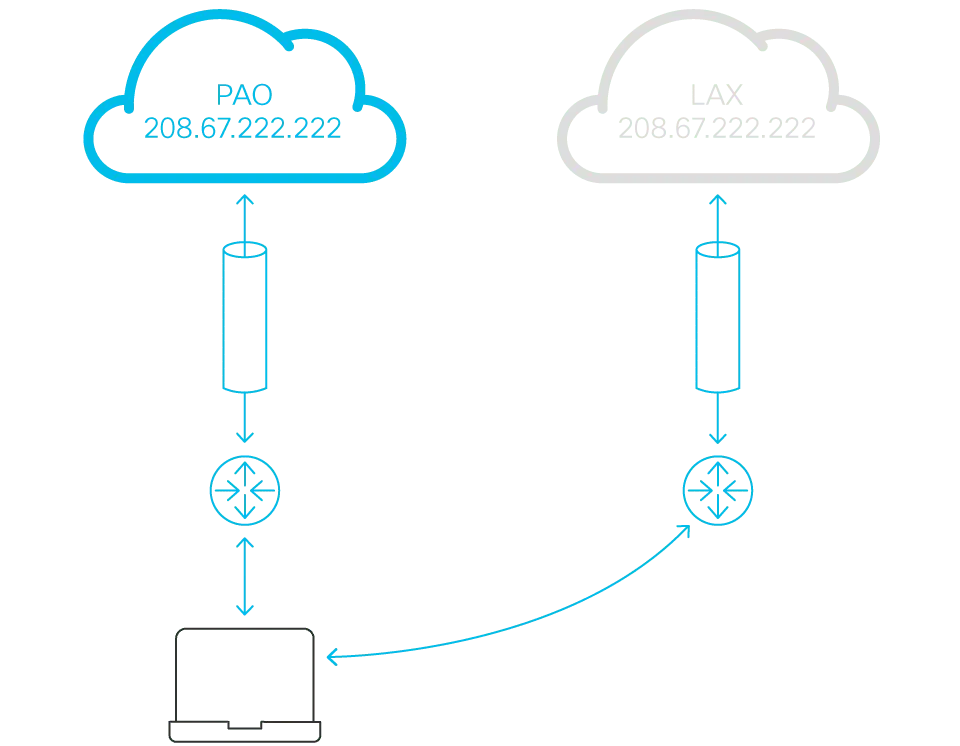
Umbrella answers lookups from anycast addresses, so your queries go to the nearest Umbrella data centre automatically. These are the Umbrella DNS IP addresses to use:
| Protocol | Primary | Secondary |
|---|---|---|
| IPv4 | 208.67.222.222 | 208.67.220.220 |
| IPv6 | 2620:119:35::35 | 2620:119:53::53 |
| DNS over HTTPS (opens in a new tab) | https://doh.umbrella.com/dns-query | Not applicable (one URL) |
Sources (checked 11 November 2026): Cisco's Umbrella documentation, Point Your DNS to Cisco Umbrella (opens in a new tab), Understand Umbrella Support for IPv6 and Configure DNS over HTTPS (DoH) with Umbrella.
Two rules matter more than anything else:
- Use only Umbrella resolvers. Do not mix in your internet provider's servers or another public DNS service as a backup. Devices pick between configured servers, so any non-Umbrella entry is a route around your policy.
- Use two different addresses. Enter both the primary and the secondary, not the same address twice. If a router insists on a third and fourth server, Cisco gives 208.67.220.222 and 208.67.222.220 (or the IPv6 pair) for those entries.
Two more points from Cisco's set-up guidance (Change your DNS server addresses, which also gives the third and fourth addresses above): some internet providers lock the DNS settings on the router they supply, in which case you configure each computer or use the roaming module instead; and Cisco does not recommend pointing email servers at Umbrella DNS.
Umbrella supports recursive IPv6 resolution and applies security and content filtering to IPv6 traffic, and IPv6 addresses can be registered as network identities. If your network runs IPv6, configure the IPv6 resolvers too, or IPv6 lookups may bypass Umbrella.
These are the same addresses the free OpenDNS service uses. Pointing at them is not enough on its own: Umbrella only applies your organisation's policy once your network is registered as an identity, as covered in the steps below. Our OpenDNS guide explains why.
Not sure which option fits? Ask us
Tell us what you need and we will recommend the right option for your organisation, with a quote.
Before you change anything
- Find out what answers DNS today. In a small office it is usually the router or firewall. With Active Directory it is your domain controllers or other internal DNS servers.
- Note your public IP address. You will register it as a network identity. If your provider changes it from time to time, plan for dynamic IP updates (Umbrella supports dynamic registration for IPv4 only).
- List your internal domains. Anything that must resolve to internal addresses, such as your AD domain or intranet names, must keep resolving locally.
- Agree a policy first. At minimum, decide which security and content categories to block. See Umbrella content filtering.
- Check your package. Network DNS forwarding, roaming and virtual appliances are available in every package; see Umbrella packages.
Point your network at Umbrella
- In the Umbrella dashboard, go to Deployments > Core Identities > Networks and add your network with its public IP address. Doing this from a device on that network is easiest. The network shows as inactive until Umbrella starts receiving its queries.
- Small office without internal DNS: on the router or firewall, set the upstream DNS servers to the two Umbrella IPv4 addresses (and the IPv6 pair if used), and make sure DHCP hands out the router or the Umbrella addresses to clients.
- Network with Windows DNS or AD: leave clients pointing at your domain controllers. On each DNS server, replace the existing forwarders with the Umbrella addresses so only external lookups go to Umbrella (our Umbrella DNS forwarders guide covers this step). For per-device and per-user reporting, put Umbrella virtual appliances in front instead.
- Dynamic public IP (IPv4 only): select the network identity and mark it as dynamic. Then either install the Umbrella Dynamic IP Updater on a desktop computer that stays on that network and is always powered on (Cisco's dynamic IP guidance), or have your router or a script send updates through Umbrella's Dynamic Network Update API when the address changes.
- Add the network to a DNS policy in the dashboard's policy section and save.
- Repeat for each site, then add the Umbrella Roaming Security Module for laptops that leave the office.
We also recommend blocking outbound DNS on your firewall to anything other than Umbrella (and your internal DNS servers), so devices with hard-coded DNS settings cannot sidestep your policy. If you use Cisco Meraki, see Umbrella and Meraki.
Is Cisco Umbrella deployment the right fit for you?
We will check it against your systems and requirements and recommend the right option.
Keep internal domains resolving locally
Never point domain-joined computers straight at Umbrella. Umbrella cannot resolve your private AD domain or internal hostnames, so logons, file shares and printers will fail.
The usual patterns are:
- Forwarders: internal DNS servers answer internal names and forward everything else to Umbrella. Simple, but Umbrella sees every query as coming from your DNS server, so reports cannot tell users or devices apart.
- Umbrella virtual appliances: the VAs forward external lookups to Umbrella and send internal domains to your internal DNS servers, while passing the internal IP address (and, with the AD Connector, the user) to Umbrella. Deploy at least two for redundancy. See the Umbrella virtual appliance guide.
Laptops running the roaming module also need your internal domains listed in the dashboard so they keep resolving them locally on the corporate network or over VPN.
DNS over HTTPS (DoH)
Modern browsers can send lookups over HTTPS to a provider of their choice, which can bypass any DNS-based filter. Umbrella offers its own DoH endpoint at https://doh.umbrella.com/dns-query, a front end for the same resolvers.
- Chrome switches to DoH automatically when secure DNS is on and it sees the Umbrella anycast addresses as the system's DNS servers. Cisco notes that it cannot do this when devices use a local DNS server or forwarder, even one that forwards to Umbrella, and that it does not switch automatically on devices Chrome treats as managed. Chrome can also be given the Umbrella URL as a custom provider.
- Firefox has its own DoH setting, separate from the system DNS. Cisco's guidance shows how to set Umbrella as Firefox's custom DoH provider with the URL above.
- Managed devices: control each browser's secure DNS setting through policy (Intune, Group Policy or the Google Admin console), either turning it off or pointing it at the Umbrella URL, so users cannot choose another provider.
- Roaming module: laptops running the Umbrella module in Cisco Secure Client already send their lookups to Umbrella, so test any browser DoH change on a pilot group first.
Chromebooks use Cisco Security for Chromebook, a Chrome extension that uses DoH to give Umbrella DNS-layer protection across the whole device. Internal domains can be excluded from Umbrella DoH with the Google Admin console's included and excluded domains setting, which Cisco's Chromebook guidance says is supported from ChromeOS 131, so they resolve through your internal DNS.
Sources (checked 11 November 2026): Cisco support document 224705, Configure DNS over HTTPS (DoH) with Umbrella, for the endpoint and the Chrome and Firefox behaviour, and Cisco's Umbrella DNS User Guide for the Chromebook setting.
Test that Umbrella is working
Once the network identity shows as active, check from a device on that network. Cisco publishes test destinations for this:
| Test site | What a working set-up shows |
|---|---|
| welcome.umbrella.com | A 'Welcome to Umbrella' page, confirming your lookups go to Umbrella |
| www.internetbadguys.com | A block page, confirming phishing protection (opens in a new tab) |
| examplemalwaredomain.com | A block page, confirming malware protection |
| examplebotnetdomain.com | A block page, confirming command-and-control protection |
| exampleadultsite.com | A block page, if your policy blocks adult content |
| proxy.opendnstest.com | Confirms the intelligent proxy, where your package includes it and it is enabled |
| ssl-proxy.opendnstest.com | Confirms SSL decryption in the intelligent proxy, where enabled |
Sources (checked 11 November 2026): Test Your Destinations in Cisco's Umbrella DNS user guide.
These destinations test DNS-layer coverage. Users who are also behind the SIG secure web gateway (opens in a new tab) or a network tunnel may see web-policy results instead, so test DNS and web policies separately. Then open the activity search in Umbrella reporting and confirm the test queries appear against the right identity. For a newly added identity, Cisco's guide to testing your DNS policies says the first report can take up to an hour to appear.
If you would like this done for you across every site, or want a second pair of eyes on an existing set-up, contact us. With Umbrella reaching end of sale on 31 January 2027, we can also check that your DNS design will carry over cleanly to Cisco Secure Access; see Cisco Umbrella end of life.
Cisco Umbrella deployment cost
Pointing your DNS at the Umbrella resolvers is part of every package, so deployment cost is the set-up work rather than an extra Cisco licence: how many networks and sites you have, whether you need virtual appliances for internal names, and which laptops need the roaming module.
Our Cisco Umbrella pricing page sets out how pricing works.
Get a quote for Cisco Umbrella deployment
Tell us what you need and we will come back to you with a quote.
How Forever Systems can help with Cisco Umbrella
We can supply and deploy Cisco Umbrella, help you run it, and plan the move to its successor, Cisco Secure Access.
- Package selection: Umbrella DNS or SIG, Essentials or Advantage, plus add-ons, matched to your users, sites and compliance needs
- Deployment: network DNS forwarding, virtual appliances, the roaming module in Cisco Secure Client, Chromebooks, IPsec tunnels from Cisco Meraki and other firewalls, and Active Directory, Entra ID or SAML identity integration
- Policy design: security categories, content filtering for schools and businesses, allow and block lists, and reporting
- Migration planning from Umbrella to Cisco Secure Access ahead of Cisco's end-of-sale and end-of-support dates
- Ongoing help: reporting, policy tuning, renewals and licence changes
Forever Systems is a Cisco Partner and also supplies the wider Cisco Secure portfolio, including Cisco Secure Access.
Frequently asked questions
What are the Cisco Umbrella DNS server IP addresses?
For IPv4, 208.67.222.222 and 208.67.220.220. For IPv6, 2620:119:35::35 and 2620:119:53::53. The DNS over HTTPS endpoint is https://doh.umbrella.com/dns-query. Use both addresses of a pair and no non-Umbrella servers.
Are the OpenDNS and Umbrella DNS servers the same?
Yes, the OpenDNS IP addresses and the Umbrella resolver addresses are shared. What makes the difference is registering your network as an identity in a paid Umbrella organisation, so your policy, reporting and subscription apply. Unregistered traffic is treated as the public OpenDNS service.
Does Umbrella support DNS over HTTPS (DoH)?
Yes. Umbrella's DoH endpoint is https://doh.umbrella.com/dns-query, a front end for the same resolvers. Control each browser's secure DNS setting through policy so users cannot pick another DoH provider and bypass Umbrella.
What are the Umbrella DNS IPv6 addresses?
2620:119:35::35 and 2620:119:53::53. Umbrella applies security and content filtering to IPv6 lookups, so configure the IPv6 pair as well as the IPv4 pair if your network runs IPv6.
How do I know if Umbrella is working?
Browse to welcome.umbrella.com from a device on the network; a working set-up shows a 'Welcome to Umbrella' page. Then try www.internetbadguys.com, which should show a block page, and check the query appears in the dashboard's activity search.
Should my domain controllers point to Umbrella?
Your domain controllers should keep answering internal names and forward external lookups to Umbrella, or sit behind Umbrella virtual appliances. Do not point domain-joined clients directly at Umbrella, or internal names will stop resolving.
Still have a question about Cisco Umbrella deployment?
Ask us and a member of our team will get back to you.
Explore Cisco Umbrella
 DeploymentStep-by-step guide to the ways Umbrella is deployed: DNS, VAs, roaming, Chromebooks, tunnels and identities.
 Virtual applianceUmbrella VAs forward external DNS to Umbrella, keep internal names local and add internal IP and AD visibility.OpenDNSOpenDNS for business: how it differs from Cisco Umbrella and how to move your networks across.
 Roaming clientThe Umbrella Roaming Security Module in Cisco Secure Client: protection for laptops off the network.
 ReportingThe Umbrella dashboard, its reports, scheduled emails, the Reporting API and S3 log export.